Free Microsoft SC-500 Practice Test Questions MCQs

Stop wondering if you're ready. Our Microsoft SC-500 practice test is designed to identify your exact knowledge gaps. Validate your skills with Microsoft Certified: Cloud and AI Security Engineer Associate questions that mirror the real exam's format and difficulty. Build a personalized study plan based on your free SC-500 exam questions mcqs performance, focusing your effort where it matters most.

Targeted practice like this helps candidates feel significantly more prepared for Microsoft Certified: Cloud and AI Security Engineer Associate exam day.

2680+ already prepared
Updated On : 12-Oct-2026
68 Questions
Microsoft Certified: Cloud and AI Security Engineer Associate
4.9/5.0

Page 1 out of 7 Pages

Topic 1: Contoso Ltd.Case Study: Contoso, Ltd.

You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!

You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.

Which role should you assign to Group1?

A. Contributor at the MG1 scope

B. Contributor at the Sub1 and Sub2 scopes

C. User Access Administrator at the MG1 scope

D. Owner at the MG1 scope

C.   User Access Administrator at the MG1 scope

You have an Azure SQL Database logical server named Server1 that contains multiple databases.

The databases contain legacy SQL authentication logins that must no longer be usable for sign-in but must NOT be removed from the databases.

You need to ensure that SQL authentication is denied for connections.

What should you do?

A. Run CREATE USER ... FROM EXTERNAL PROVIDER on each database.

B. Create a Conditional Access policy.

C. Enable Microsoft Entra-only authentication for Server1.

D. Assign the SQL Server Contributor role to Server1.

C.   Enable Microsoft Entra-only authentication for Server1.

You have an Azure subscription named Sub1 that contains a storage account named storage1. Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has malware scanning enabled.

You need to configure a solution that automates the remediation of malware detected in storage1.

What should you include in the solution?

A. Application Insights

B. Azure Event Hubs

C. Azure Event Grid

D. Azure Policy

C.   Azure Event Grid

You have an Azure Storage account named storage1 that hosts a blob container named container1.

You have an Azure Functions app named app1 that uses a managed identity.

You need to configure app1 to read, write, and delete blobs in container1. The solution must follow the principle of least privilege.

What should you do?

A. Assign the Storage Account Contributor role to the managed identity of app1 at the scope of storage1.

B. Assign the Storage Blob Delegator role to the managed identity of app1 at the scope of container1.

C. Assign the Owner role to the managed identity of app1 at the scope of container1.

D. Assign the Storage Blob Data Contributor role to the managed identity of app1 at the scope of container1.

D.   Assign the Storage Blob Data Contributor role to the managed identity of app1 at the scope of container1.

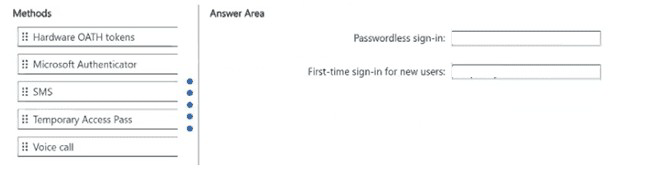
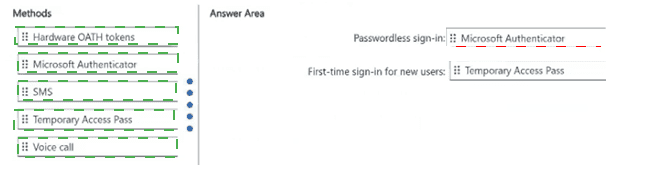
You have a Microsoft Entra tenant.

You need to implement password less authentication. The solution must meet the following requirements:

•Users can sign in without a password by using a mobile device.

•New users that sign in for the first time must use a helpdesk issued sign in method that expires.

Which authentication method should you enable for each requirement? To answer, drag the appropriate methods to the correct requirements. Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.

NOTE: Each correct selection is worth one point.

You have an Azure subscription.

You need to deploy an Azure virtual WAN to meet the following requirements:

•Create three secured virtual hubs located in the East US. West US, and North Europe Azure regions.

•Ensure that security rules sync between the regions.

What should you use?

A. Azure Network Function Manager

B. Azure Firewall Manager

C. Azure Virtual Network Manager

D. Azure Front Door

B.   Azure Firewall Manager

You have a hybrid environment that contains the following servers:

•50 Azure virtual machines that run Windows Server 2019

•20 physical, on premises servers that run Windows Server 2019

All the servers use a third-party antivirus solution that must remain active during a phased security rollout

You need to onboard all the servers to Microsoft Defender for Endpoint by using a centralized deployment method. The solution must meet the following requirements:

•Endpoint detection and response (EDR) capabilities must be enabled.

•Antivirus conflicts must be prevented during onboarding.

What should you do on the servers?

A. Set the Microsoft Defender for Endpoint service to Disabled.

B. Disable Microsoft Defender Antivirus real-time protection by using Set-MpPreference.

C. Configure the ForceDefenderPassiveMode registry value.

D. Enable EDR in block mode.

C.   Configure the ForceDefenderPassiveMode registry value.

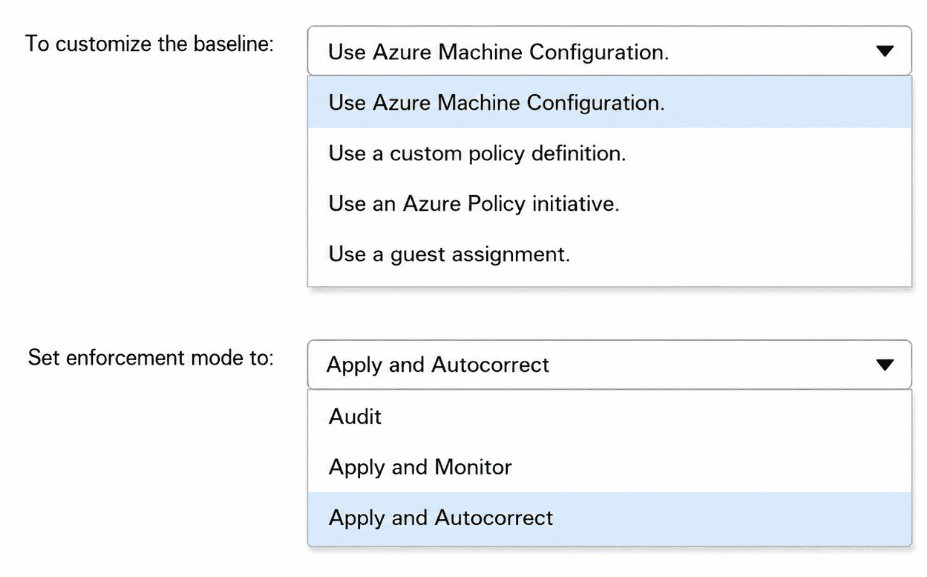
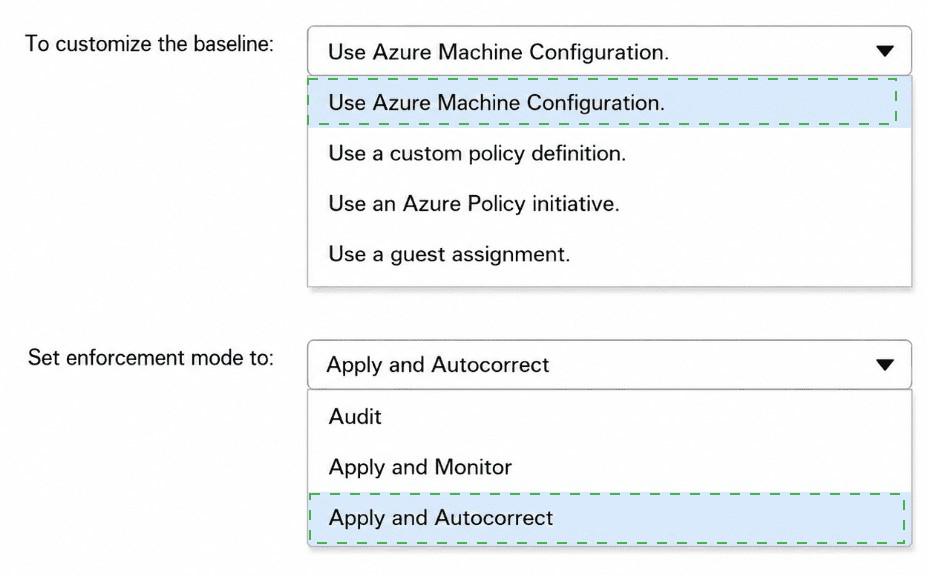
You have an Azure subscription that contains the following servers:

•200 virtual machines that run either Windows Server or Ubuntu Server

•50 Azure Arc enabled servers

You use Azure Policy to manage compliance across all the servers.

You need to enforce an organization-specific security baseline. The solution must meet the following requirements:

•Customize a built-in security baseline.

•Ensure that configuration changes to the servers are enforced automatically after the security baseline is deployed.

Minimize administrative effort.

What should you do? To answer, select the appropriate options in the answer area.

NOTE: Each correct selection is worth one point.

You are configuring a new Microsoft Sentinel workspace named Workspace1.

You have an external IT Service Management (ITSM) system that is NOT supported by any Microsoft Sentinel solutions in Azure Marketplace.

You need to ensure that Workspace1 creates service tickets in the ITSM system for all new security incidents.

What should you create?

A. A playbook

B. A workbook

C. A watchlist

D. An analytics rule

A.   A playbook

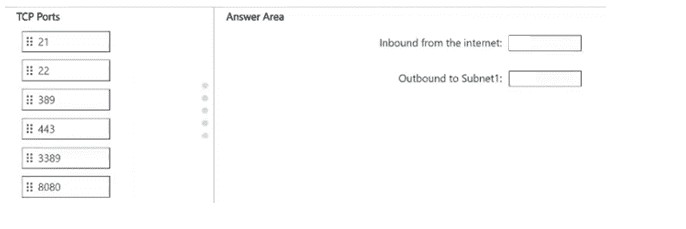
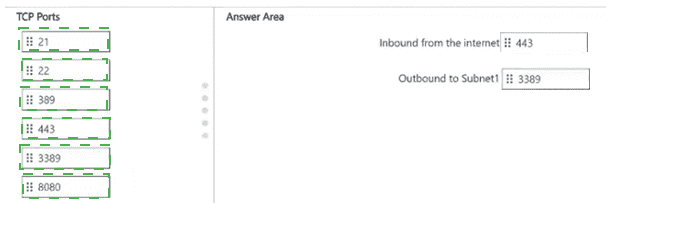
You have an Azure virtual network named VNet1 that contains an Azure Bastion Subnet.

VNet1 contains a subnet named Subnet1 Subnet1 contains multiple virtual machines.

You plan to deploy Azure Bastion to provide secure RDP access to the virtual machines on Subnet1. You associate a network security group (NSG) named NSG1 to Azure Bastion Subnet.

You need to configure rules for NSG1. The solution must meet the following requirements:

•Allow required inbound access to Azure Bastion from the internet.

•Allow user access to the virtual machines by using Azure Bastion.

Which TCP ports should you allow for the NSG1 rules? To answer, drag the appropriate ports to the correct rules. Each port may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.

NOTE: Each correct selection is worth one point.

Page 1 out of 7 Pages
123

Microsoft Certified: Cloud and AI Security Engineer Associate Practice Exam Questions